Blog & Research

Attack techniques. Misconfiguration patterns.

Technical writeups on cloud offensive security from the people who build the labs.

4 articles

LatestTechniques

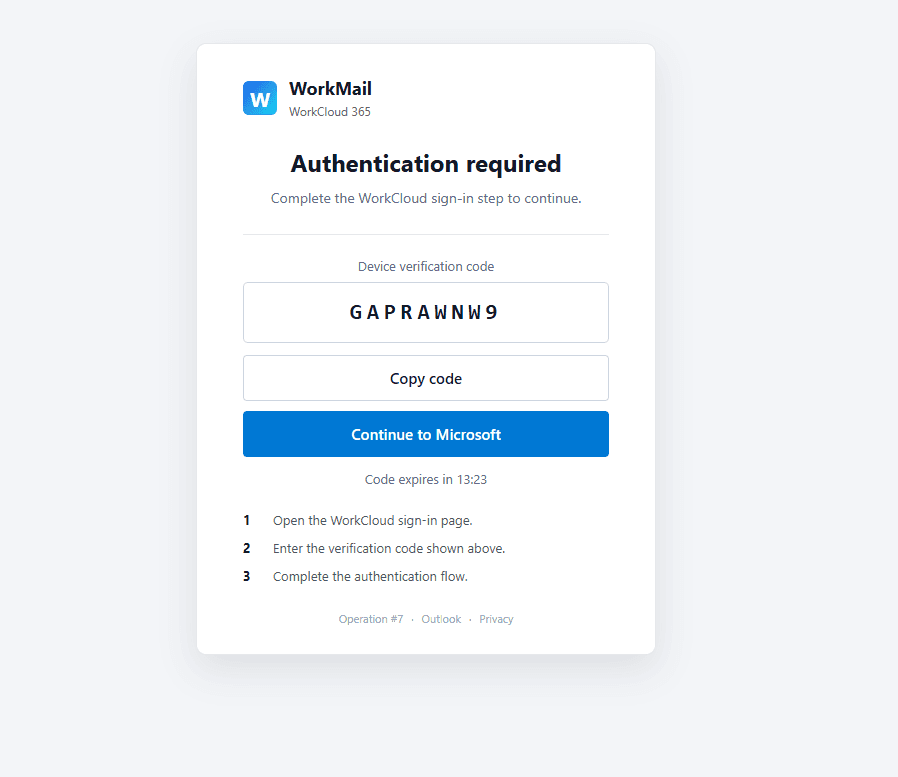
Device Code Phishing: Skipping the Password, Registering the Device

An MFA bypass with no fake login page: the victim completes a real Microsoft sign-in, and the attacker walks away with a live session. Abusing the Authentication Broker client can turn that session into a registered device and a Primary Refresh Token.

8 min read
Read the article
More articles

AWS

Intro To AWS Enumeration – Part 1

Unauthenticated AWS S3 enumeration through the lens of an adversary: OSINT with Google and GitHub dorks, Shodan and FOFA queries, technology fingerprinting, and finding open buckets with uncover and nuclei.

5 min read
Research

EnvWatch: Find Exposed Cloud Secrets Before Hackers Do

A practical tool for scanning your local machine for exposed API keys, AWS credentials, private keys, and .env files, before an attacker does it for you.

10 min read
Misconfigurations

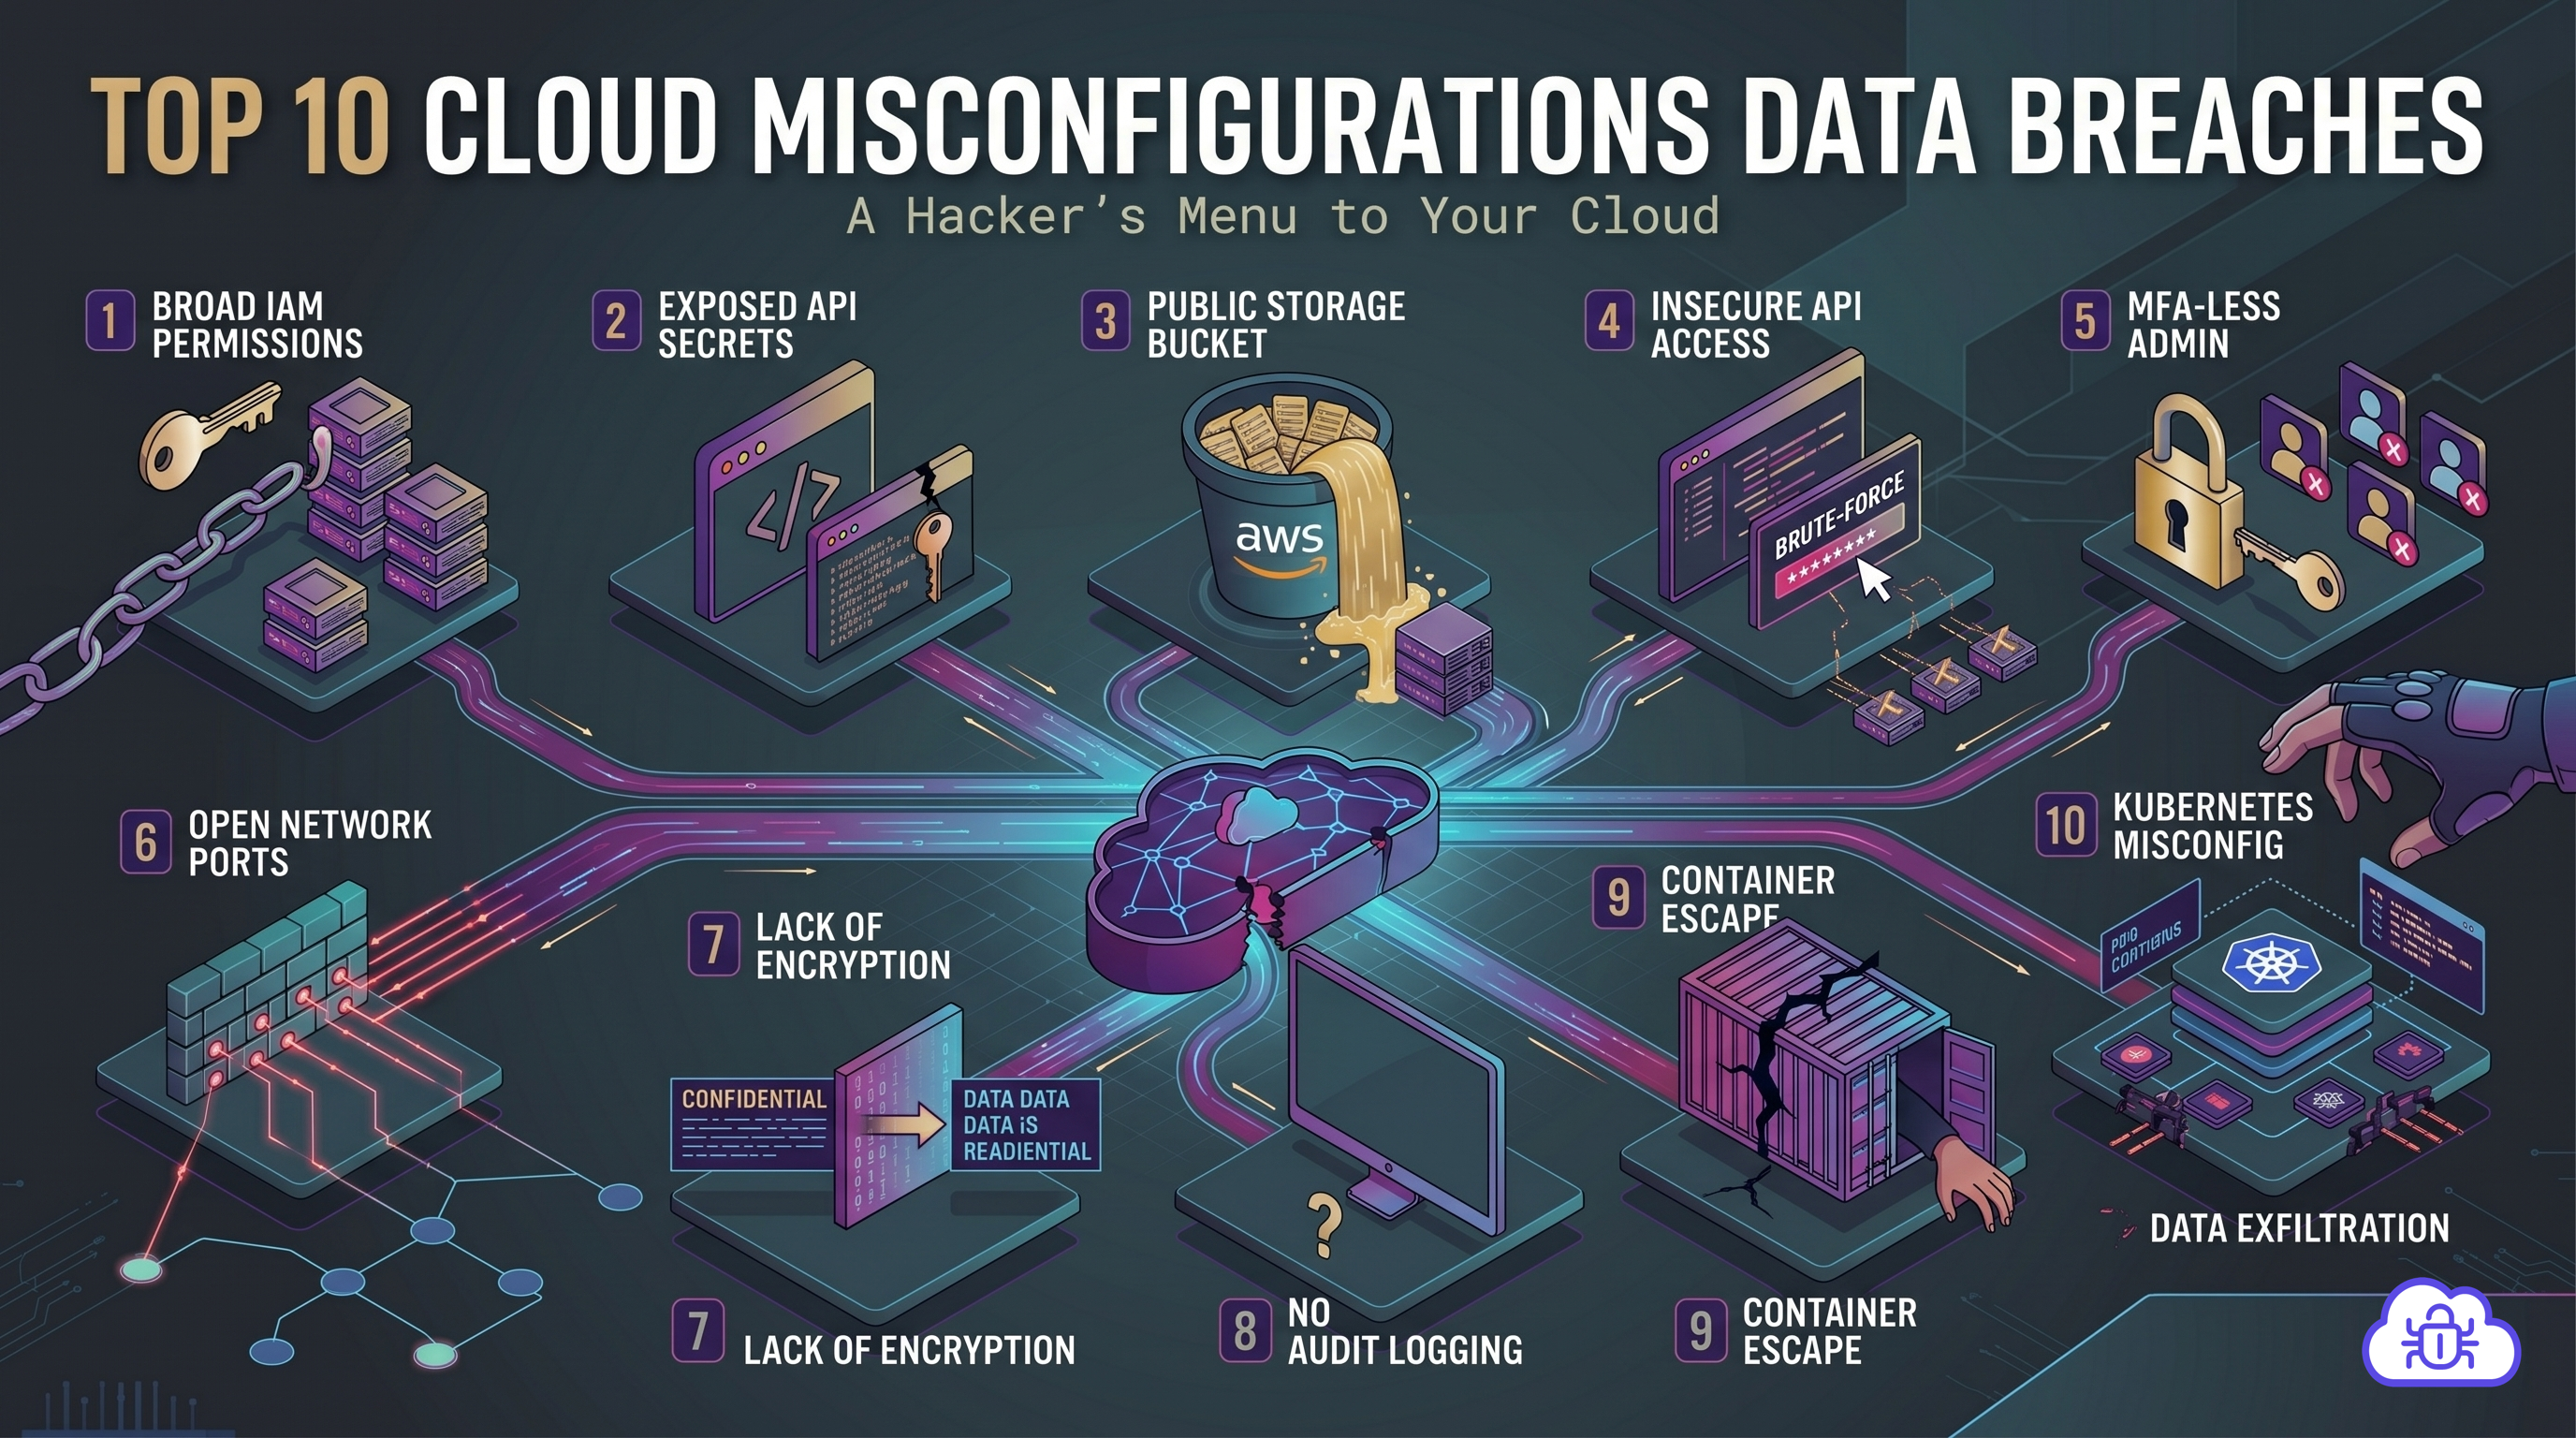
Top 10 Cloud Misconfigurations That Lead to Data Breaches

Most cloud breaches aren't zero-day exploits, they're misconfigurations. We break down the 10 most common cloud security mistakes with MITRE ATT&CK references and remediation guidance.

6 min read